Threat Actor Profile: "Chucky" – Administrator of LeakBase
Threat Actor Summary
| Attribute | Details |
|---|---|
| Threat Actor Alias | Chucky |
| Other Aliases | Chuckies, Sqlrip, beakdaz |
| Primary Role | Administrator of LeakBase cybercrime forum |
| First Observed Activity | 2013 |
| Primary Platform | LeakBase cybercrime forum |
| Associated Platforms | LeakBase and Telegram |
| Primary Activity | Facilitation and distribution of breached databases, credential collections, and stealer logs |
| Operational Model | Subscription-based access to leaked data and cybercrime marketplace services |
| Target Scope | Global |
| Motivation | Financial gain |
| Current Status | Infrastructure dismantled during an international law enforcement operation in 2026 |
Introduction
“Chucky” is a cybercriminal actor associated with the administration and operation of the cybercrime forum LeakBase, a platform dedicated to the distribution and sale of stolen databases and compromised credentials. The actor is believed to have become active around 2021, however, earlier indicators of online activity date to 2013 (Flare, 2023).
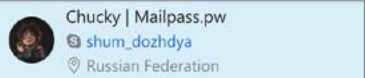
Researchers published a detailed attribution analysis, assessing with high confidence that Chucky, the alias “beakdaz”, and the LeakBase administrator are all the same individual — an actor linked to Taganrog, Russia, with cybercrime activity dating back to 2009 (KELA, 2026).
It is speculated that Chucky operates from Russia. This assessment is based on researchers identifying a Skype account believed to be associated with the actor (Virus Bulletin, 2023).
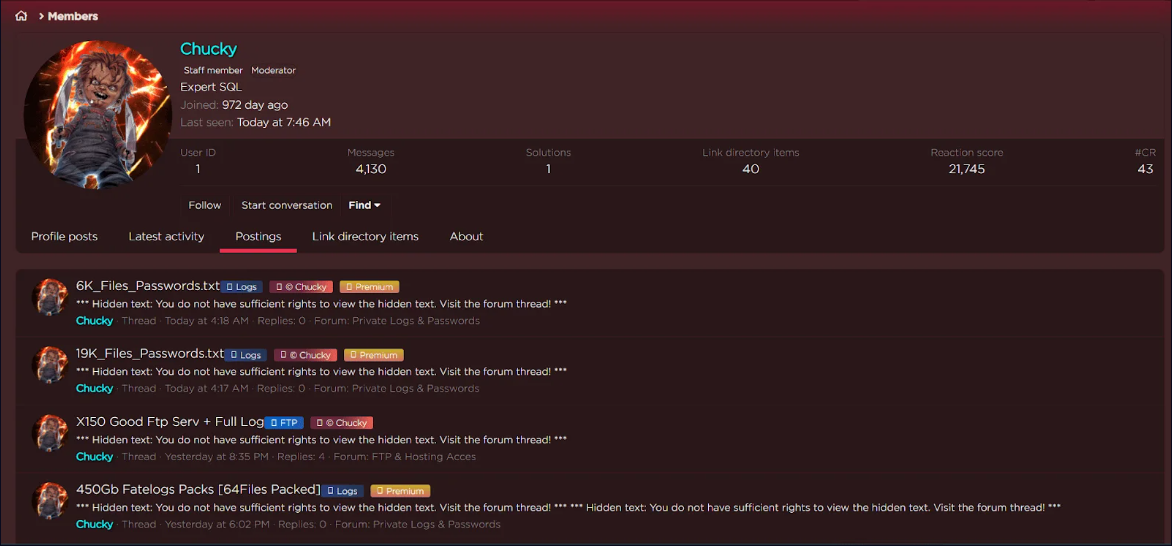
LeakBase operated primarily as an English language forum that facilitated the exchange of compromised data between cybercriminal actors. The platform allowed users to share and sell breached datasets, including personal information, authentication credentials, and stealer logs collected from infected systems. By 2025, LeakBase reportedly had approximately 142,000 registered users, highlighting its scale within the cybercrime ecosystem (Cybernews, 2025).
“Chucky” has been associated with several aliases across cybercrime forums, including “Chuckies” and “Sqlrip”, suggesting attempts to maintain a presence across multiple platforms and identities (Flare, 2023). In addition to the forum itself, Chucky reportedly maintained associated Telegram channels used to distribute data leaks and communicate with members of the cybercrime community (Virus Bulletin, 2023).
Notable breaches published by Chucky include DELL and Tappware.
In March 2026, LeakBase was dismantled during a coordinated international law enforcement operation, which resulted in the seizure of the forum’s infrastructure and the confiscation of its database of users and administrators (Computing, 2026).
Modus Operandi (MO)
Chucky’s activities primarily involved operating and maintaining infrastructure used to facilitate cybercrime, rather than conducting intrusions directly.
LeakBase functioned as a marketplace for breached information, allowing cybercriminal actors to upload, advertise, and distribute stolen data. The platform utilised a structured forum environment where users could browse leak categories, request datasets, or promote newly acquired breach material.
Data commonly hosted or distributed through LeakBase included:
- Database dumps
- Credential logs
- Stealer logs
- Hacking guides and services
- Breach announcements and data leak disclosures
Many of these datasets originated from vulnerabilities in web applications, misconfigured databases, or successful network intrusions conducted by third-party threat actors (Computing, 2026).
The forum employed a tiered subscription model, where users could pay for enhanced access to datasets or premium content. This monetisation model enabled Chucky and other administrators to generate revenue through the facilitation of illicit data trading.
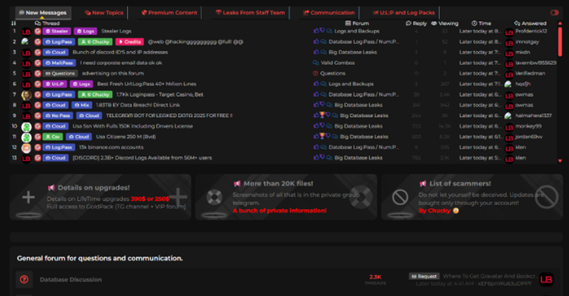
LeakBase was also notable for being accessible on the clear web, rather than exclusively on the dark web, which reduced barriers to entry and broadened the platform’s user base (Cybernews, 2025).
Tactics, Techniques and Procedures (TTPs)
The behaviour associated with Chucky and the operation of LeakBase demonstrates several common tactics and procedures used by administrators of cybercrime marketplaces.
Infrastructure Management
- Administration of a cybercrime forum dedicated to leaked databases
- Hosting of breach announcements and leak repositories
- Maintenance of user accounts and forum moderation
Data Distribution
- Facilitation of the sale and sharing of stolen datasets
- Distribution of credential collections and stealer logs
- Organisation of breach data into searchable forum categories
Communication Channels
- Use of Telegram channels to distribute leaks and engage with community members
- Utilisation of encrypted or pseudonymous communication platforms for transactions and contact (Virus Bulletin, 2023)
Monetisation
- Implementation of subscription tiers for access to premium leaks
- Use of cryptocurrency-based payments for services and data access
Operational Security (OPSEC)
- Use of multiple online aliases across cybercrime forums
- Separation between infrastructure operators and data suppliers
- Reliance on pseudonymous identities and decentralised communication channels
Reputation within the Cybercrime Ecosystem
LeakBase gained recognition within cybercrime communities as a significant repository of breached data and credential collections. Security monitoring organisations identified the forum as a notable data leak marketplace due to the scale of information available and its active user base (Computing, 2026).
The forum’s appeal was partly derived from its structured marketplace format, which allowed cybercriminals to efficiently browse and acquire compromised data. Reports indicate that LeakBase hosted datasets containing hundreds of millions of compromised credentials and financial records originating from multiple breaches.
Despite its popularity, the reputation of Chucky within underground communities appears to have been mixed. As the forum gained notoriety, instances emerged where other actors attempted to impersonate or leverage the Chucky identity to conduct scams or fraudulent activities (SpyCloud, 2024).
Notably, in August 2025, Chucky claimed to have breached DarkForums, a rival cybercrime forum, and began publishing the data on his Telegram channel. The attack was allegedly carried out in response to AnonSec defrauding Russian users out of cryptocurrency.
Conclusion
Chucky represents a type of cybercriminal actor whose role focuses primarily on enabling and facilitating cybercrime rather than conducting direct attacks.
By operating LeakBase, the actor created an environment where stolen data could be easily distributed, monetised, and exchanged between threat actors. Platforms such as LeakBase contribute significantly to the cybercrime ecosystem by providing a structured marketplace that incentivises the theft and resale of sensitive information.
The international law enforcement operation that dismantled LeakBase demonstrates an increasing emphasis on disrupting cybercriminal infrastructure, which can have broader impacts on the underground economy than targeting individual attackers alone.
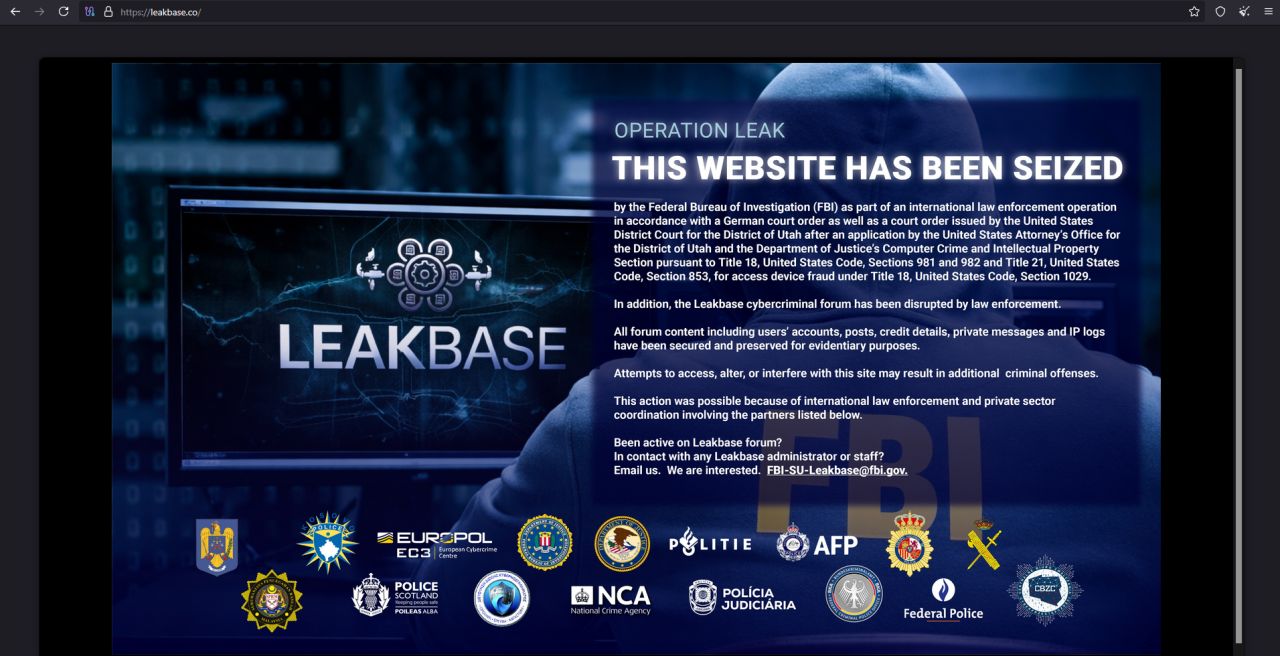
However, given the persistent demand for compromised data within cybercrime communities, it is highly likely that similar forums and marketplaces will emerge to replace LeakBase, continuing the cycle of illicit data trading.
References
- KELA Cyber Intelligence Center. (2026). Law enforcement seizes LeakBase.
- Computing. (2026). Cybercrime forum LeakBase dismantled in international law enforcement operation.
- Cybernews. (2025). LeakBase cybercrime forum taken down by authorities.
- Flare. (2023). Top cybercrime forums monitored by threat intelligence analysts.
- SpyCloud. (2024). Cybercrime underground activity update.
- Virus Bulletin. (2023). Sheep’s clothing: The deep dark web operators hiding in plain sight.